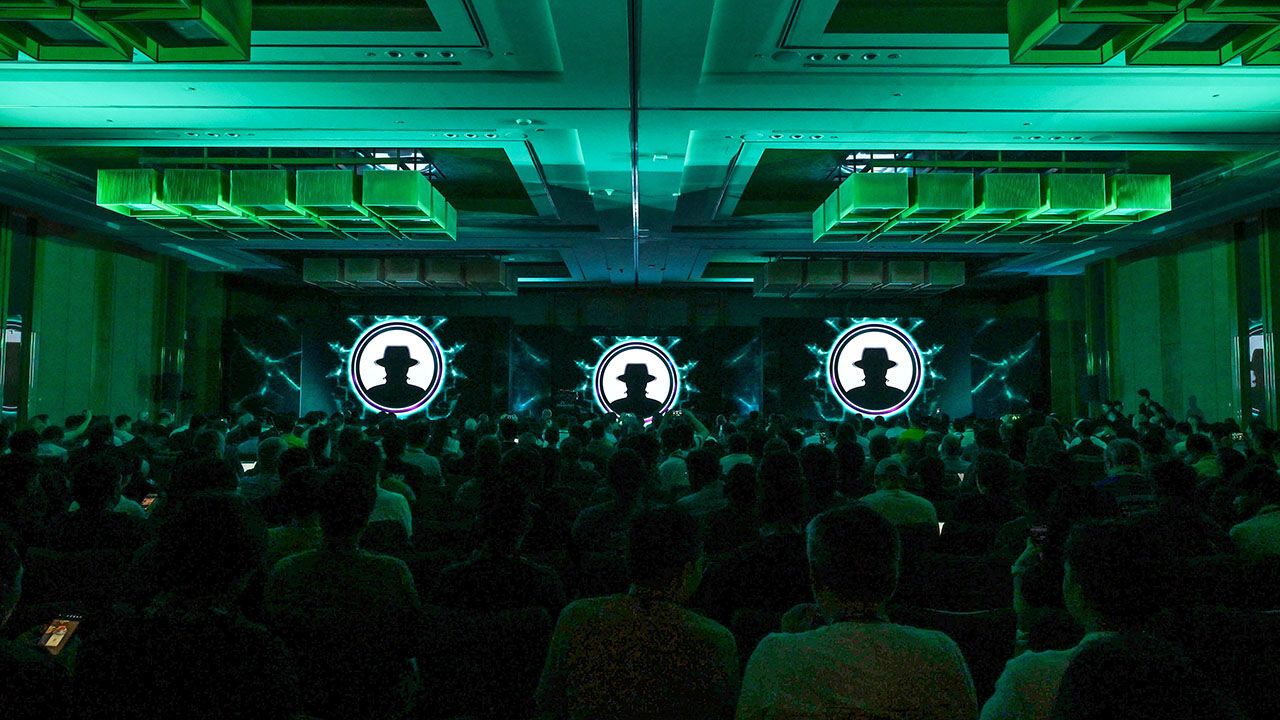
IT TAKES ONLY a brief chat with the organisers of Black Hat Asia to realise this is no ordinary conference. Whereas most professional get-togethers invite their guests to piggyback on(蹭用;搭便车) the hotel Wi-Fi, Black Hat builds the network for its annual conferences in Las Vegas, London and Singapore from scratch(从零开始), installing switches, access points, firewalls and monitoring sensors before the conference opens. The Network Operations Centre (NOC) must then defend it in real time from thousands of the world’s best hackers—not just the conference’s adversaries(对手;敌人), but also those attending, who are explicitly tasked with attacking its infrastructure.
只需稍作交谈,就能意识到Black Hat Asia并非普通会议。大多数专业会议邀请客人蹭用酒店Wi-Fi,而Black Hat则从零开始为在拉斯维加斯、伦敦和新加坡举行的年度会议搭建网络,在会议开幕前安装交换机、接入点、防火墙和监控传感器。网络运营中心(NOC)必须实时抵御成千上万全球顶尖黑客的攻击——不仅是会议的外部敌人,还有与会者,他们被明确要求攻击会议的基础设施。
This year’s Singapore edition, held from April 21st to 24th, took place in the shadow of(在……的阴影之下) announcements from large tech companies that artificial-intelligence models could now outperform all but(几乎;除了……都) the best hackers. Anthropic’s Mythos, for example, the most prominent such model, is already said to have identified severe vulnerabilities in “every major operating system and web browser”. For most tech users, this feels like a watershed moment(分水岭时刻). For those at Black Hat, however, it is confirmation of what they have long seen coming.
今年4月21日至24日的新加坡会议,是在大型科技公司宣布人工智能模型现已超越除最顶尖黑客之外的所有人的阴影下举行的。例如,其中最著名的Anthropic公司的Mythos,据称已经识别了“每一个主要操作系统和网络浏览器”中的严重漏洞。对大多数技术用户来说,这感觉像是一个分水岭时刻。然而对于Black Hat的参与者而言,这只是对他们长久以来预见的确认。
Defending Black Hat is “orders of magnitude(数量级)” harder than ordinary corporate cyber-security, says Neil “Grifter” Wyler who has run the NOC for 24 years, all but 6 of which have been alongside his colleague Bart Stump(除6年外都与其同事一起). Indeed, when the head of cyber-security for the Paris Olympics needed a model for his own security-operations centre, he spent a week with the NOC at Black Hat London. Part of the challenge is scale: a typical firm faces one or two attackers at a time whereas Black Hat must deal with thousands, many testing exploits(攻击手法;漏洞利用代码) freshly taught by world-class instructors. The other challenge is filtering: the NOC team must allow such coursework to happen while distinguishing it from real attacks.
经营NOC已达24年的Neil "Grifter" Wyler(其中除6年外一直与同事Bart Stump共事)表示,防御Black Hat比普通企业网络安全难“几个数量级”。事实上,当巴黎奥运会的网络安全负责人需要为自己的安全运营中心寻找模型时,他在Black Hat London的NOC待了一周。挑战之一在于规模:典型企业一次面临一两个攻击者,而Black Hat必须应对数千人,其中许多人测试着世界级讲师刚教授的攻击手法。另一个挑战是筛选:NOC团队必须允许这类课程活动发生,同时将其与实际攻击区分开来。